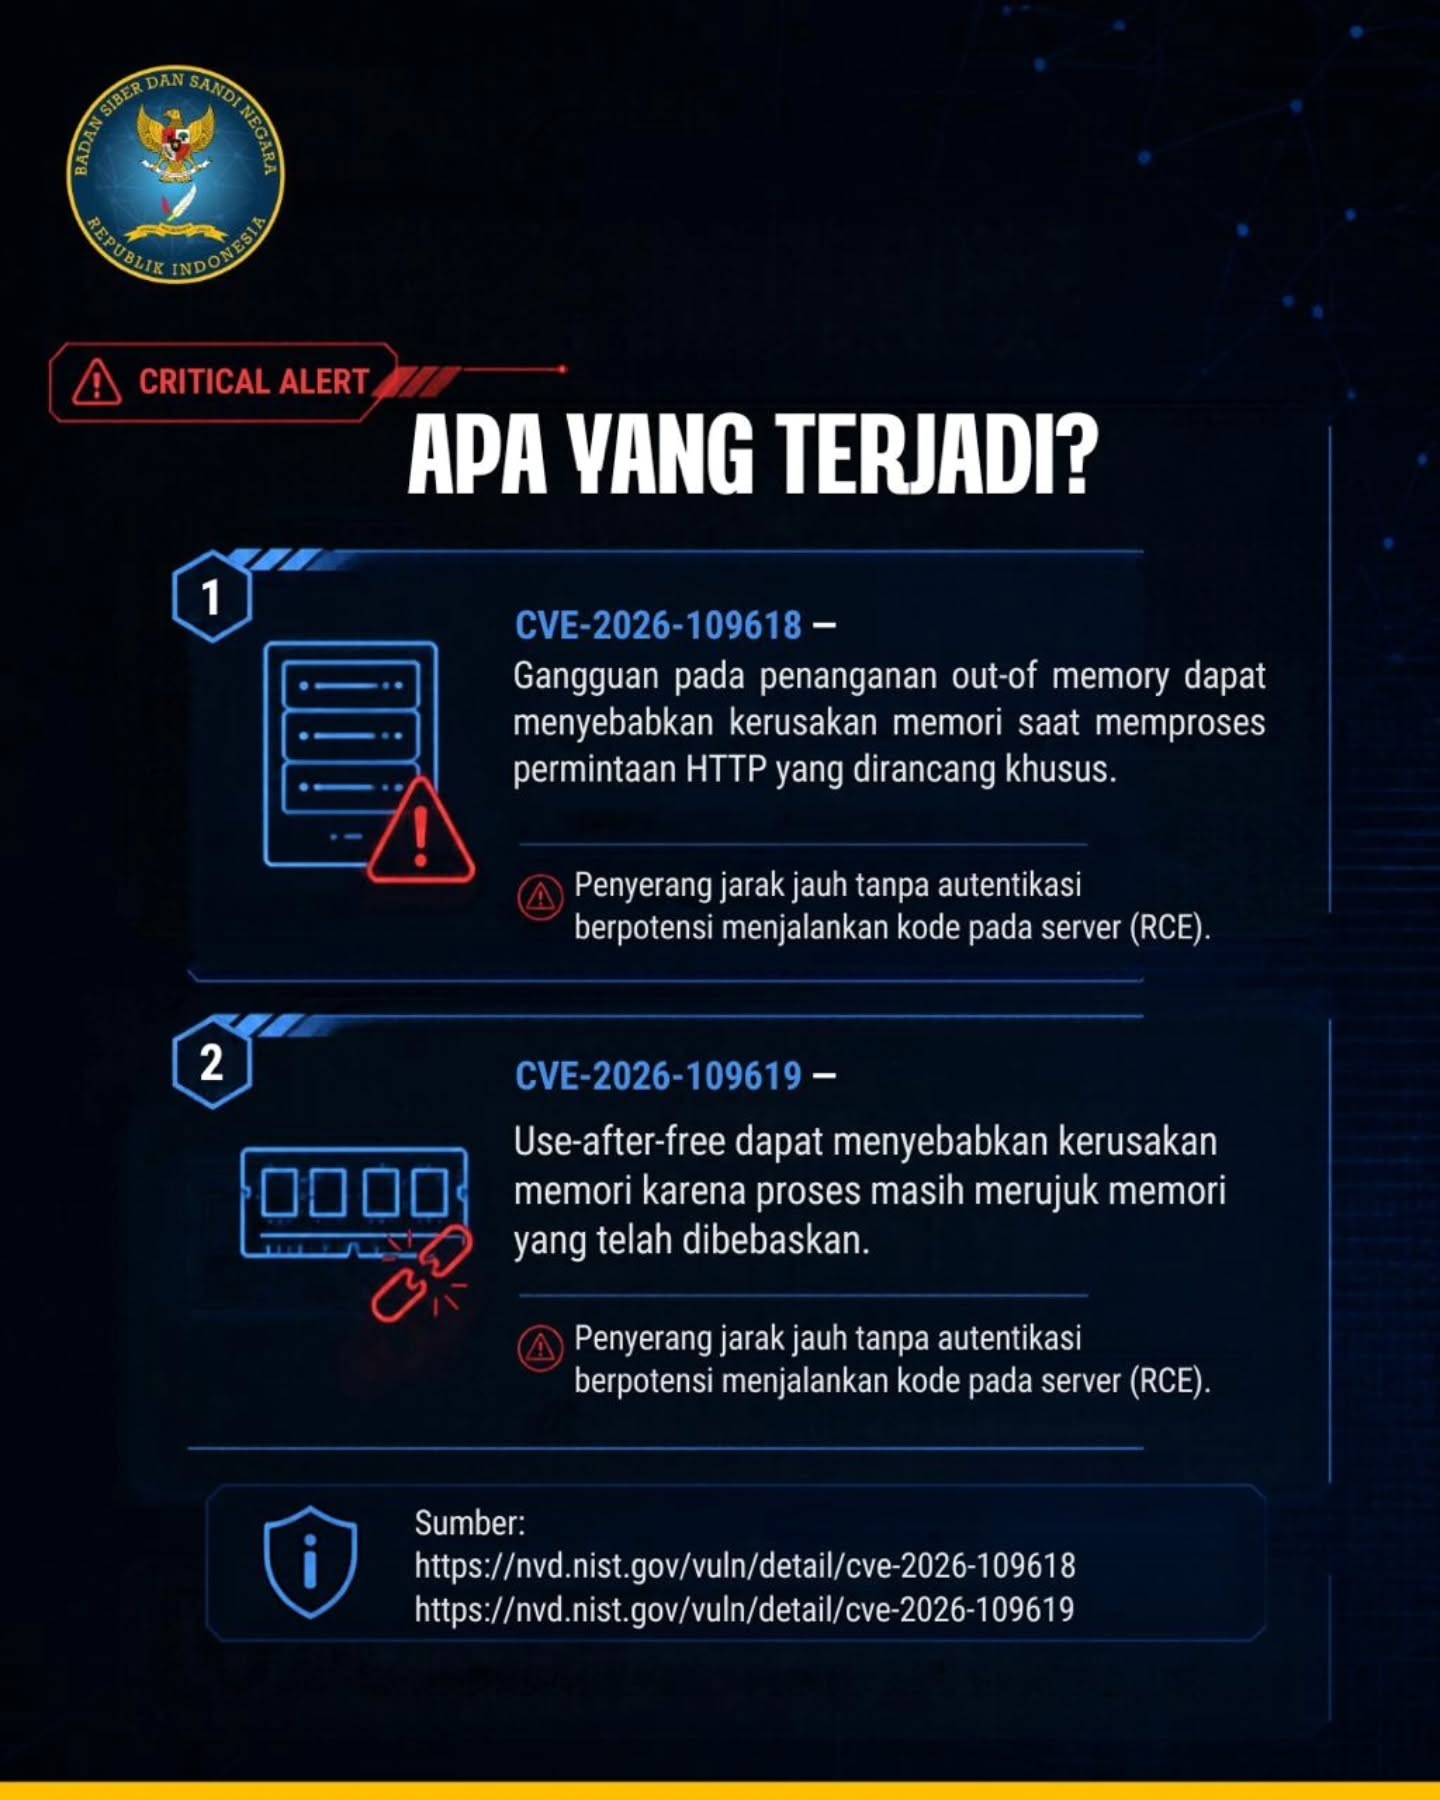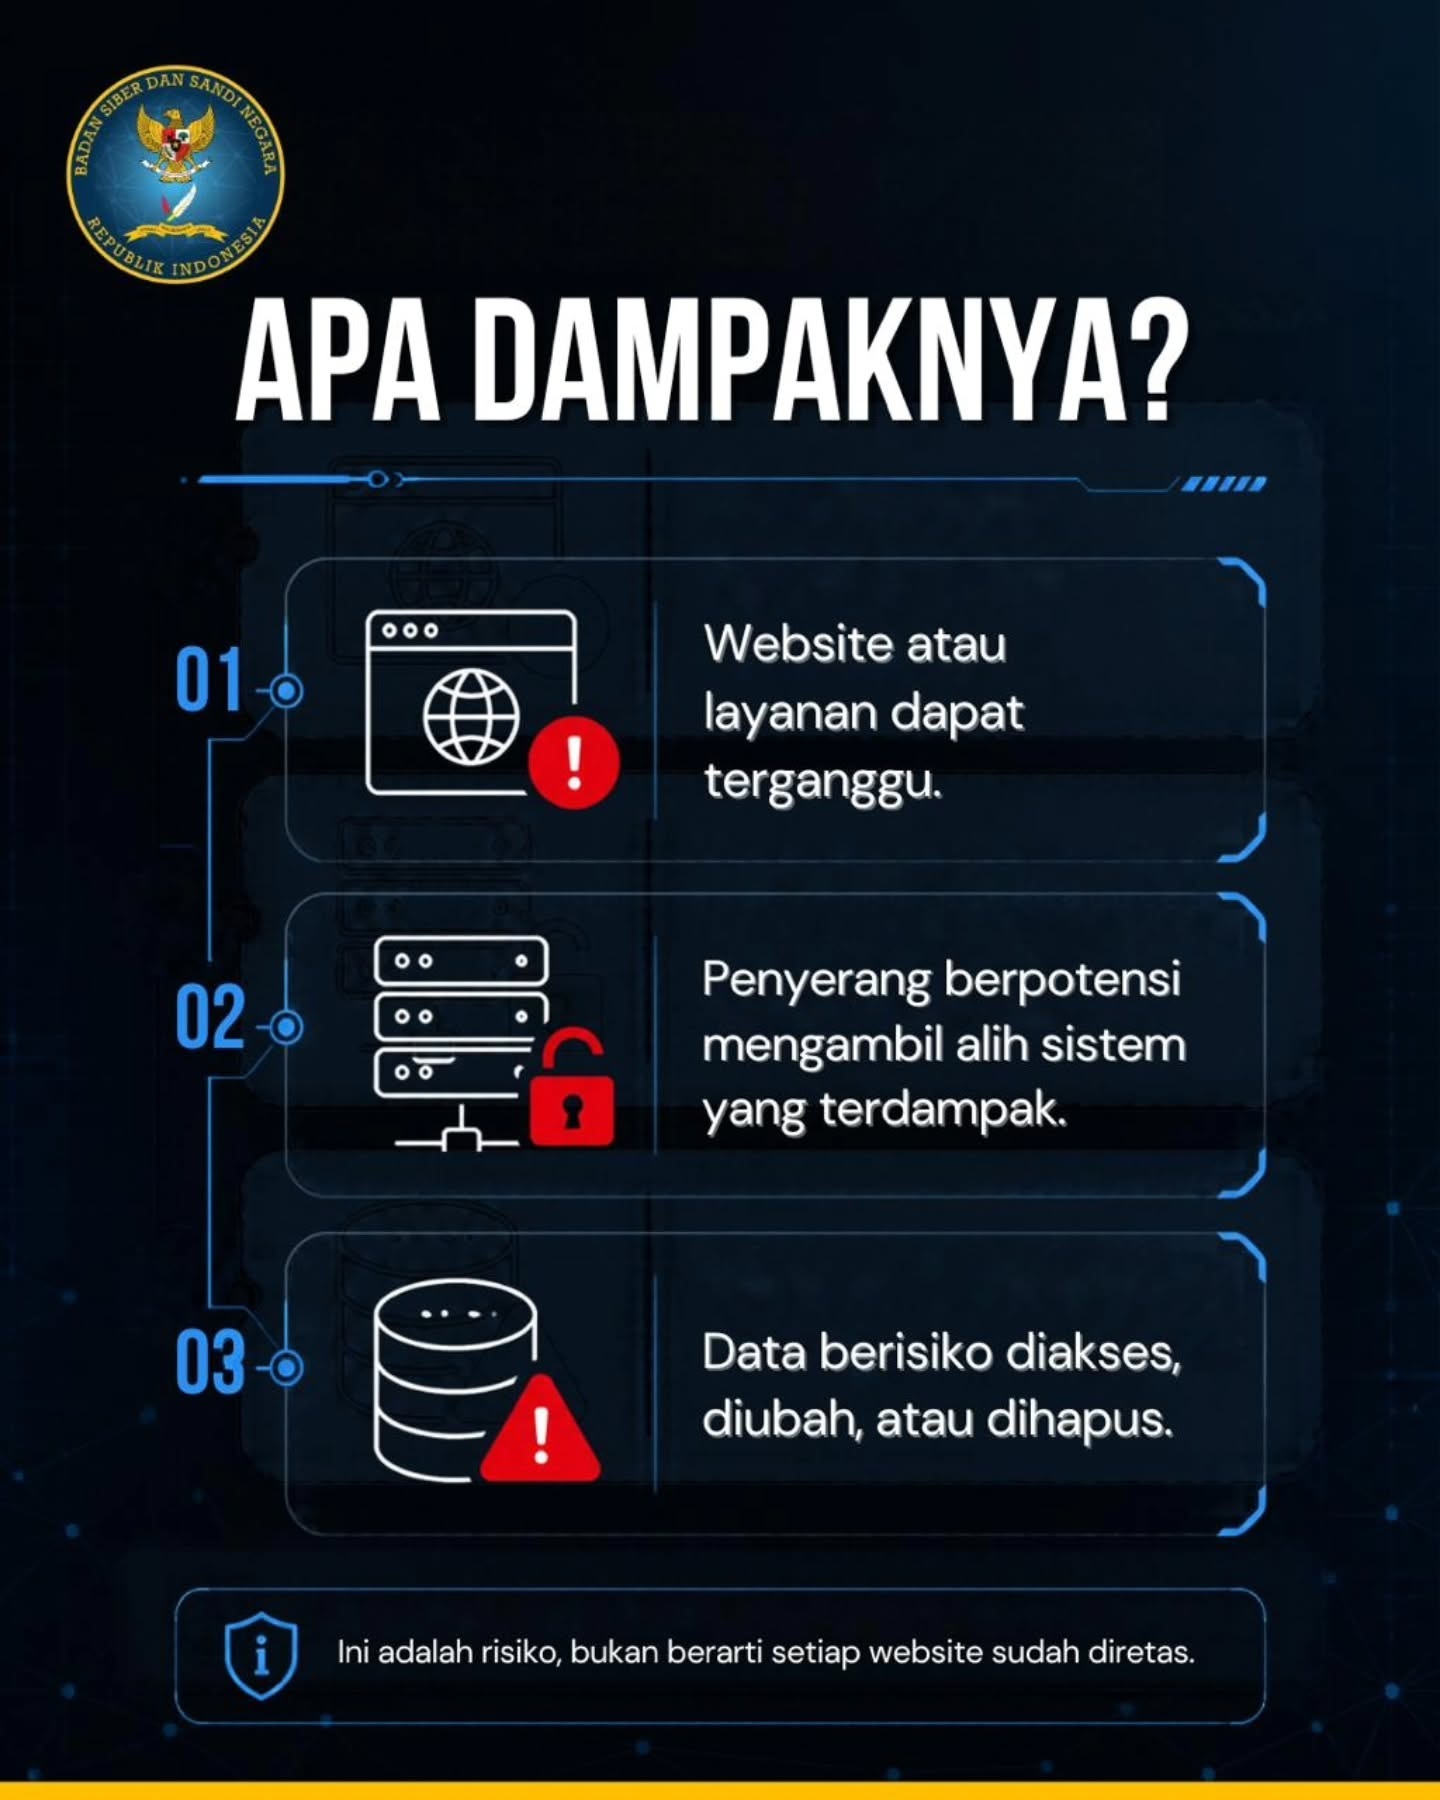
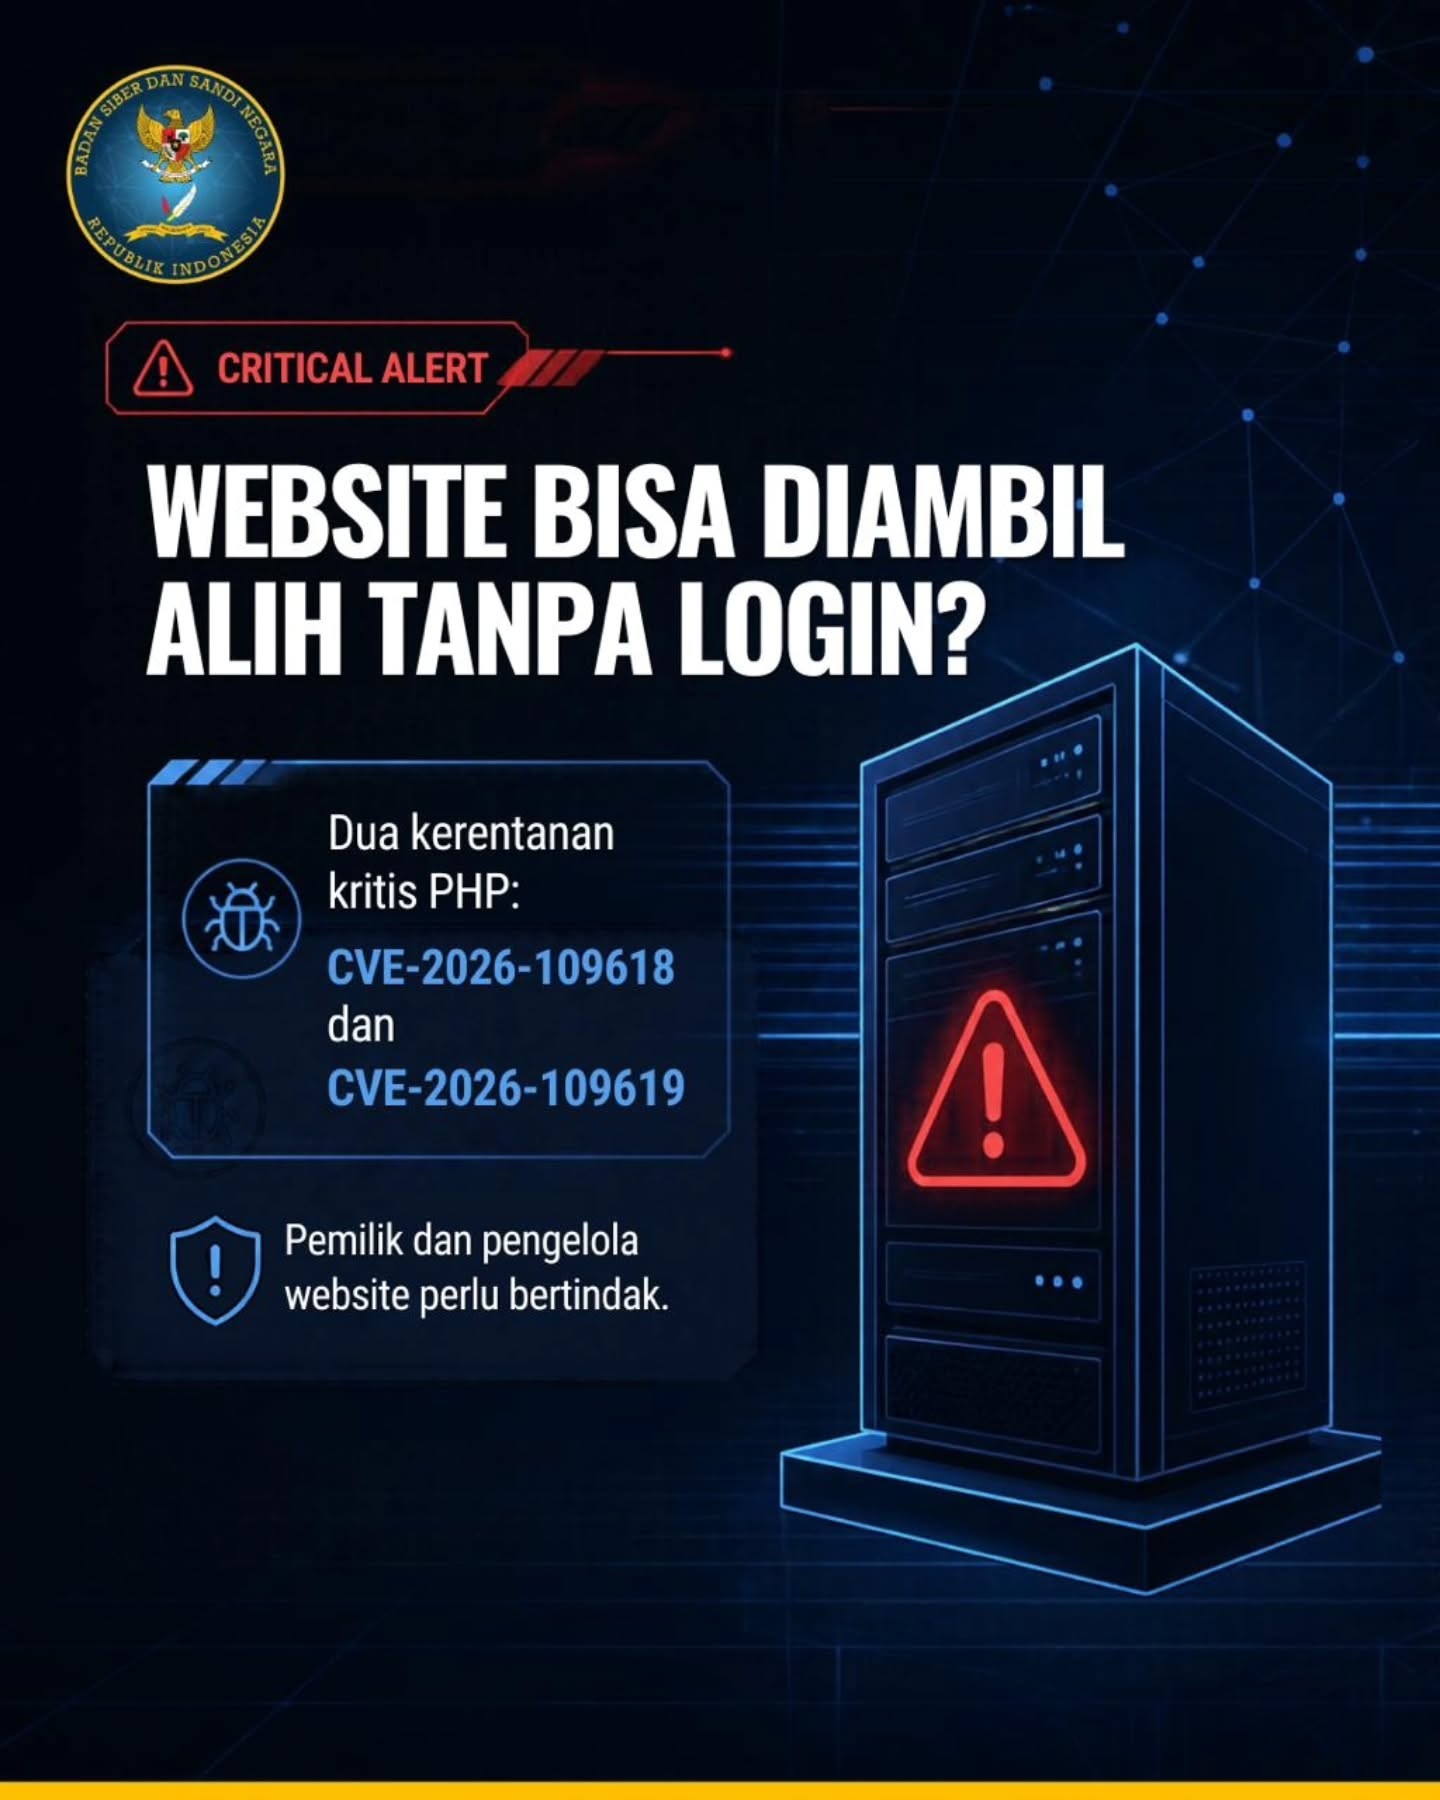
CVE-2026-109618 is a discovery of a vulnerability in the out-of-memory (OOM) handling mechanism in PHP that can cause memory corruption when processing HTTP requests. An unauthenticated remote attacker could send HTTP requests specifically designed to trigger these conditions and potentially exploit PHP processes to perform Remote Code Execution (RCE) on an affected server. CVE-2026-109619 is a use-after-free vulnerability in PHP resulting from access to memory that has been freed, but is still referenced by the process's internal state. This condition can cause memory corruption and has the potential to be exploited by remote attackers without authentication to perform Remote Code Execution (RCE) on the affected server. Successful exploitation depends on request processing conditions and PHP environment configuration.
Products Threatened:
- PHP 8.5 version < 8.5.12
- PHP 8.4 version < 8.4.27
- PHP 8.3 version < 8.3.36
- PHP 8.2 version < 8.2.35
- PHP 8.1 and earlier versions are potentially affected and have EOL status
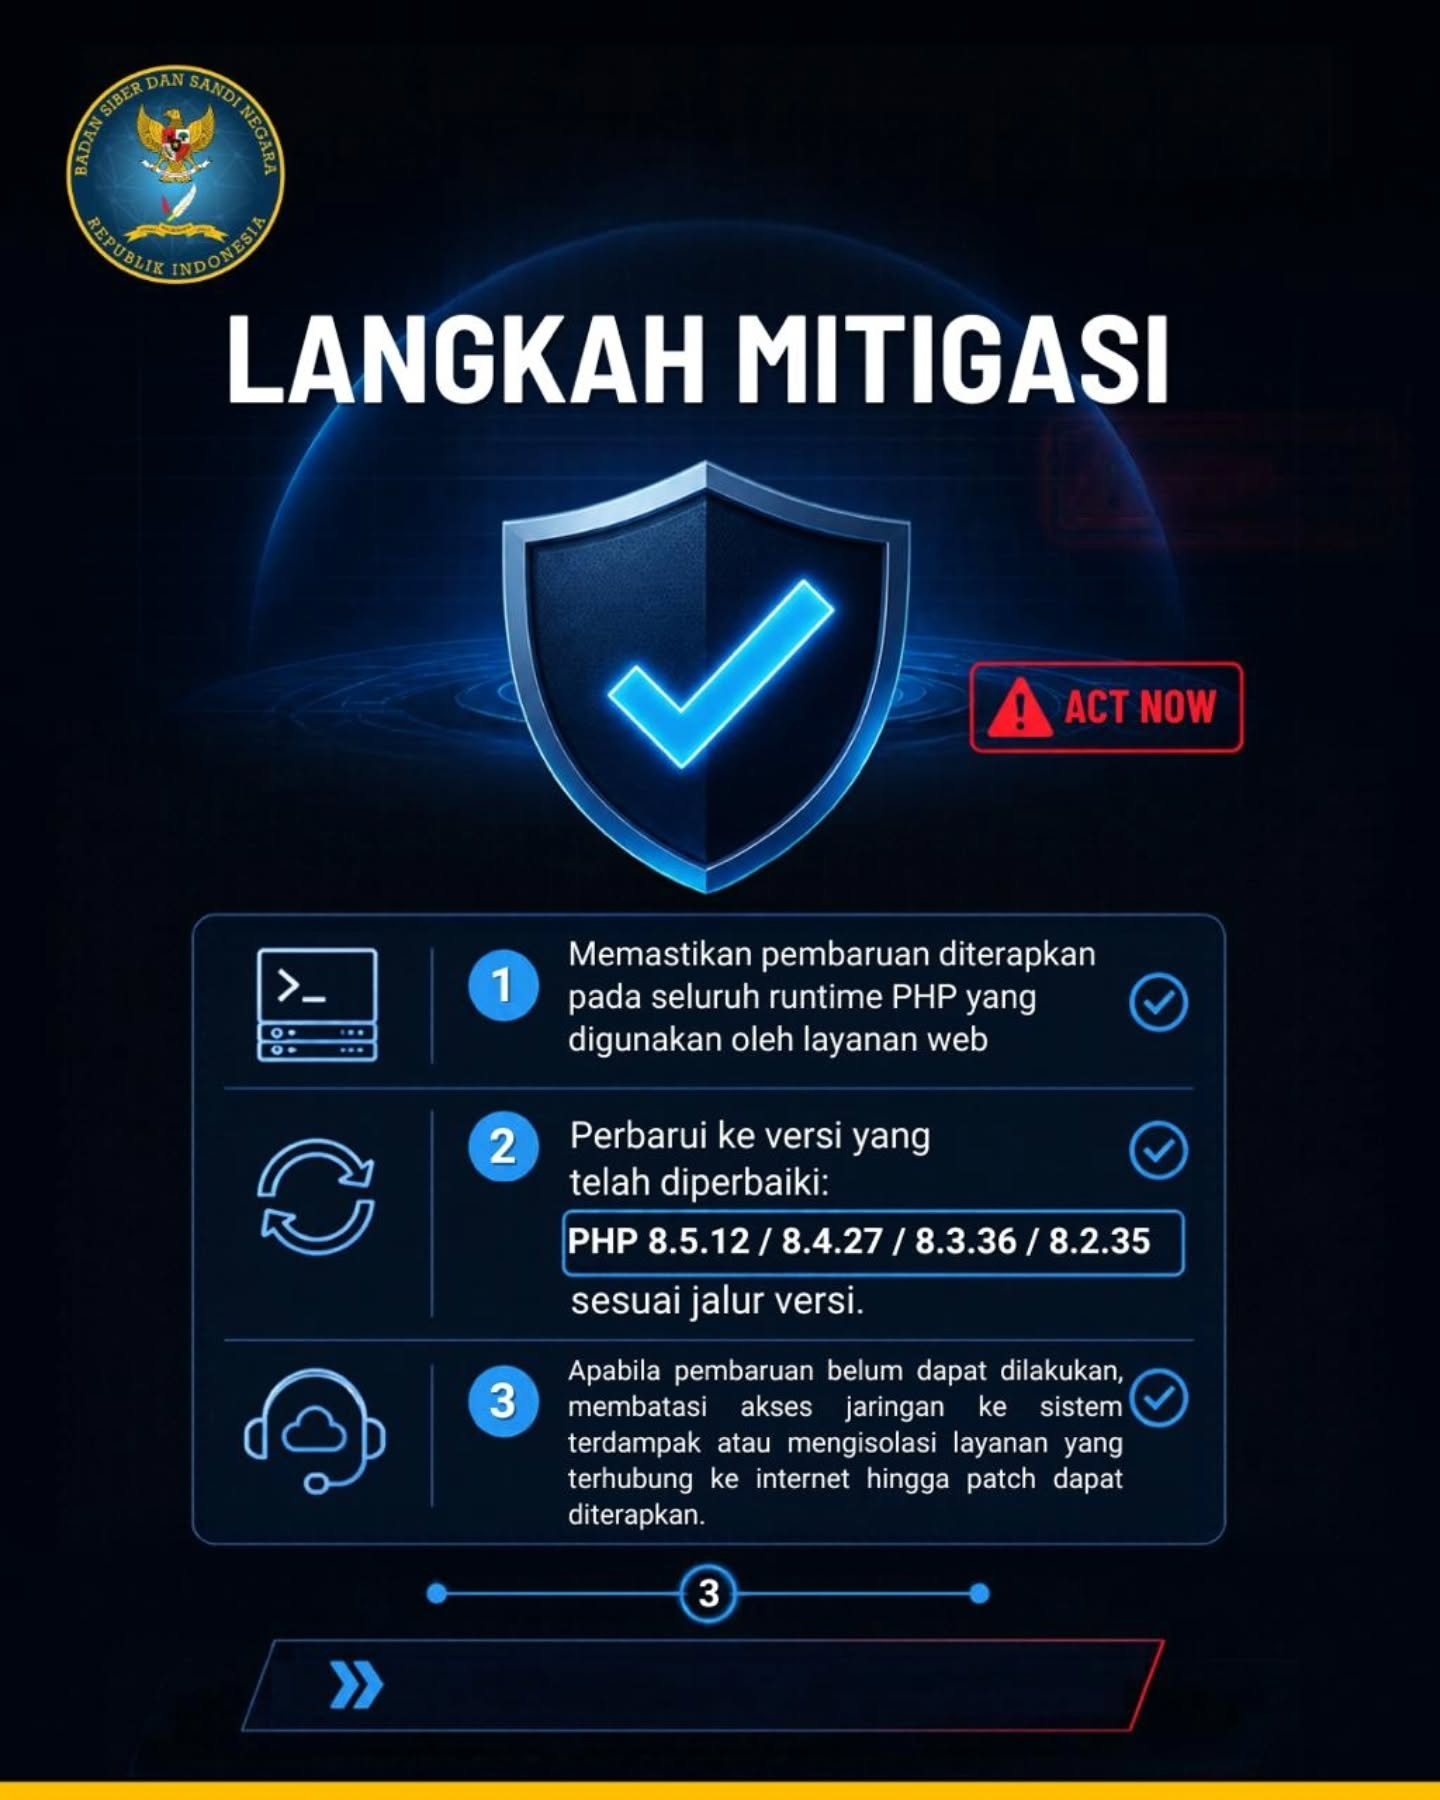
Mitigation Steps:
- Update PHP to version which has been fixed, namely PHP 8.5.12, 8.4.27, 8.3.36, or 8.2.35, according to the version used.
- Ensures updates are applied to all PHP runtimes used by web services, including PHP-FPM, Apache mod_php, and php-cgi, as well as restarting related services after the update.
- If the update cannot be performed, limit network access to the affected system or isolate internet-connected services until the patch can be applied.
Publication Documents: Security Advisory : Vulnerabilities in PHP2Shell (CVE-2026-109618 & CVE-2026-109619)